Classic Engine Feature EOL: SSR, Desktop SSO, Device Trust
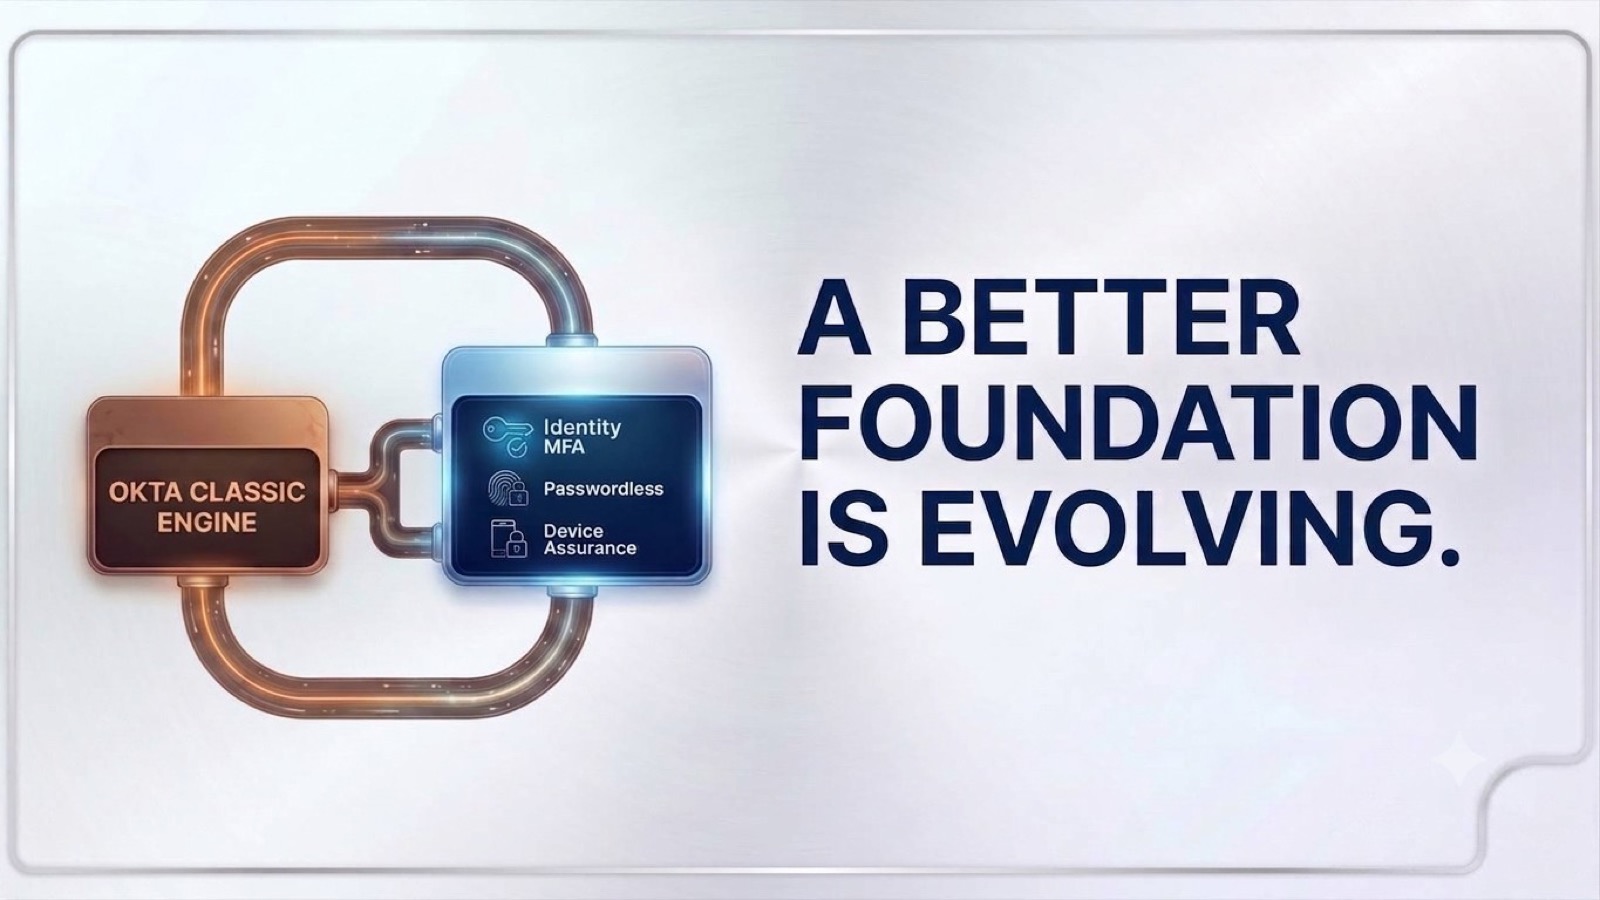
Starting March 5, 2027, Okta ends support for a few capabilities on Classic Engine. Identity and security requirements continue to evolve. Organizations expect authentication experiences that are more secure, flexible, and adaptable to changing users, devices, and applications. Okta invests in Okta Identity Engine, the modern foundation for passwordless authentication, device assurance, phishing-resistant multifactor authentication, and adaptive security policies. By moving to Okta Identity Engine, you access an environment aligned with modern security practices that...
Supercharge Auth with Signals and the New Okta Angular SDK
Have you noticed that the Okta Angular SDK went fully standalone? There’s no NgModule left to import, no importProvidersFrom wrapper to remember, and the guards are plain functions now. If you’ve been waiting for the SDK to look like the rest of your standalone Angular app, this is the release you were waiting for. In this post, we’ll pick up a small Angular v22 project and finish it. We’ll make the following changes: Add authentication...
Add Cross App Access to Your OIDC Resource Application
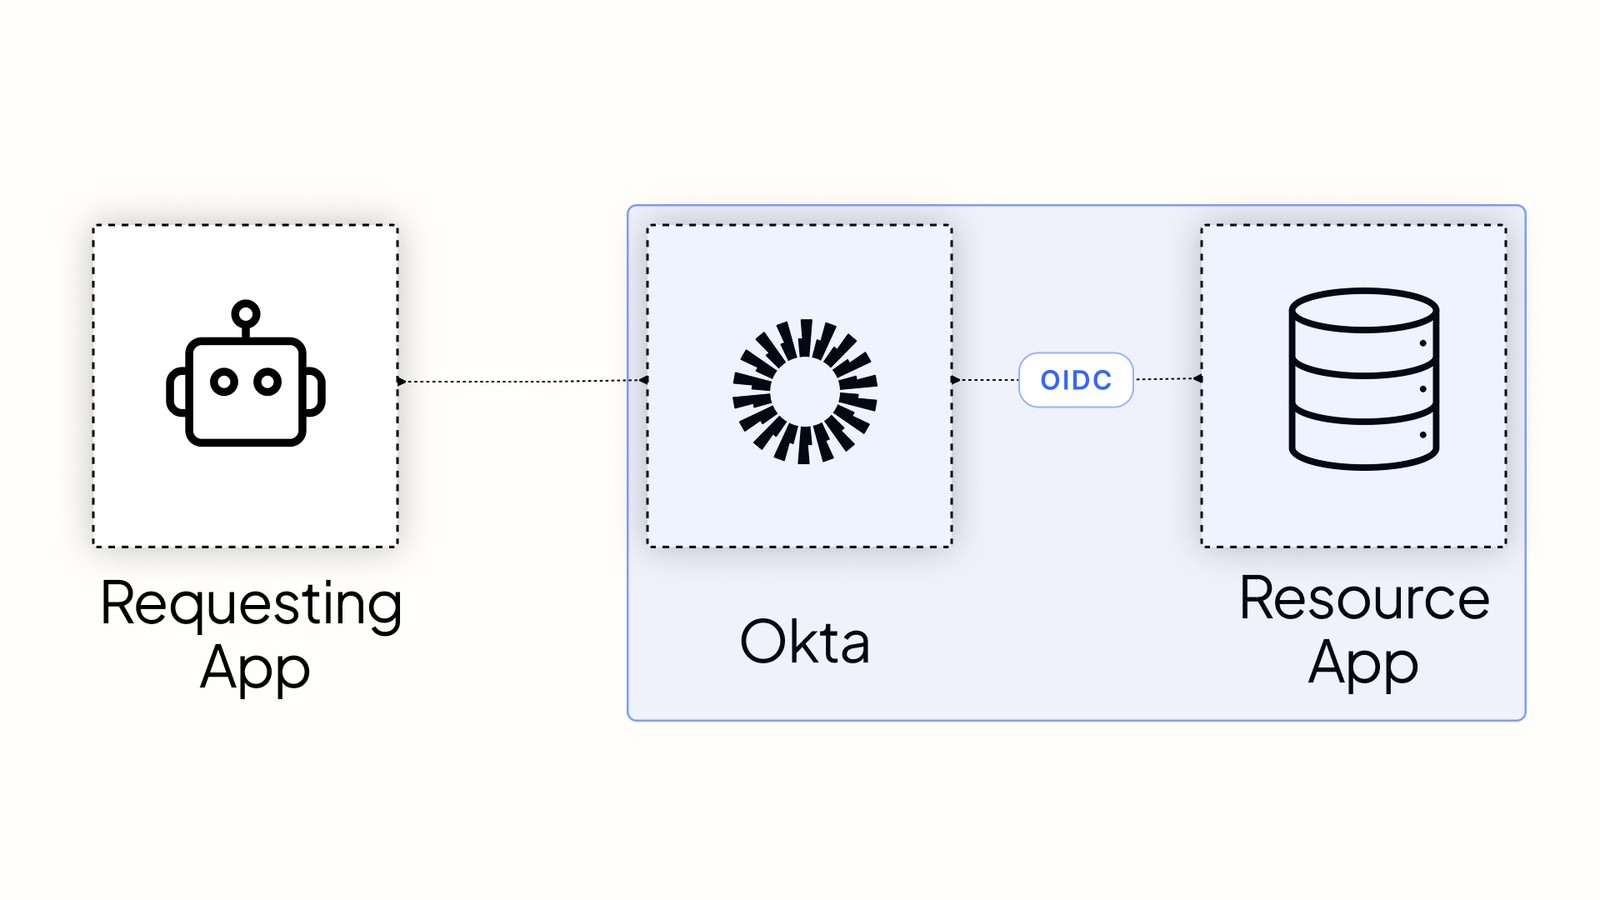
If you currently federate enterprise customers using OpenID Connect (OIDC) and want to allow applications to access your API on behalf of those users, this Cross App Access (XAA) guide is for you. The Identity Assertion Authorization Grant specification, the basis of XAA, was designed with OIDC in mind. Your authorization server already trusts the customer’s IdP for single sign-on (SSO), and XAA reuses that same trust for API access. This guide details what you...
Add Cross App Access to Your OIDC Requesting Application
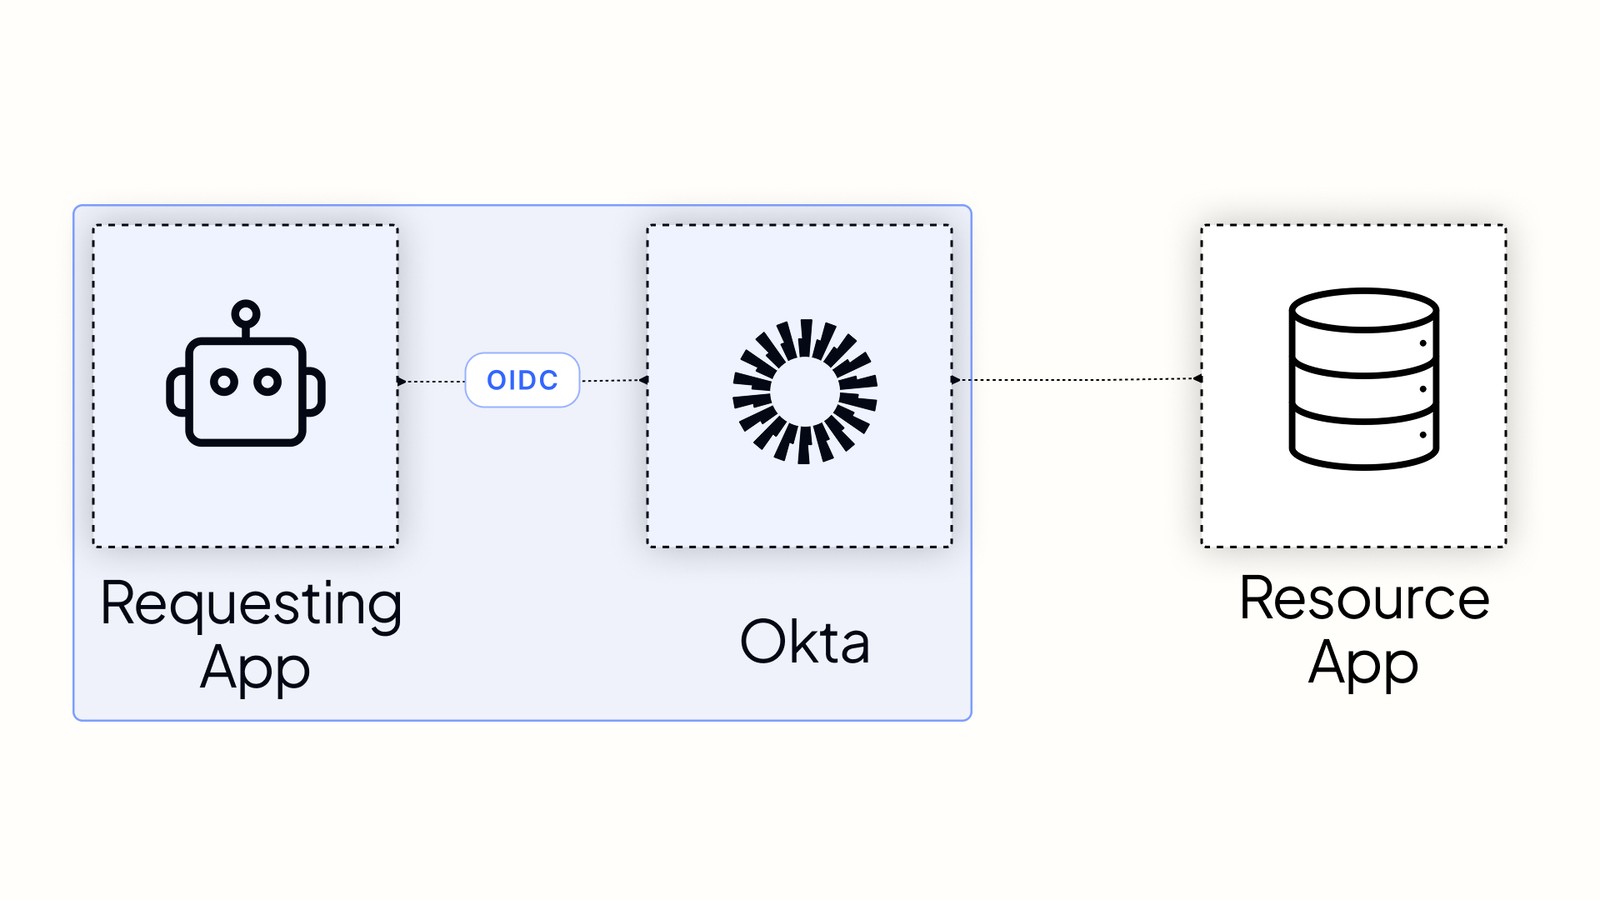
If you currently federate enterprise customers using OpenID Connect (OIDC) and want to connect with third-party applications, this Cross App Access (XAA) guide is for you. The Identity Assertion Authorization Grant specification, the basis of XAA, was designed with OIDC in mind. Your app already holds an ID token after sign-in, but it’s the refresh token from that same sign-in that you exchange to reach a third-party app. This guide details what you need to...
I Found My Coordinates: Code, Community, and Okta

It all started with a phone call from an institute that reached out to recruit me for its campus ambassador program. I was navigating my first year of college, figuring things out. It was all new for me, a new city, far from home, and a hostel room. I was not aware of anything except books and lectures. A senior at my campus ambassador program advised me to create a LinkedIn account and start looking...
Build a Flask App with Okta for Secure OIDC Login and Authorized API Calls
Python syntax and the flexibility of the Flask microframework make it a popular choice for quickly building web applications. While Flask provides the essentials to get you started, you’ll need to tackle two critical pieces yourself: secure user authentication and authorization for your backend services. After all, how do you securely sign users into your application? And once they’re signed in, how does your app fetch data from a backend service that only serves authorized...
Enable Your SAML Requesting App for Cross App Access
If you currently federate enterprise customers using Security Assertion Markup Language (SAML) and want to connect with third-party applications without migrating to OpenID Connect (OIDC), this Cross App Access (XAA) guide is for you. The Identity Assertion Authorization Grant specification, the basis of XAA, was originally designed with OIDC in mind. To use it in SAML applications, you must accommodate specific security and uniqueness requirements. This guide details what you need to support and how...
Build a Secure C# MCP App with Cross App Access (XAA)
A few years ago, getting a user signed in to an application or multiple applications with Single Sign-On (SSO) was enough; OpenID Connect (OIDC) handled the login, JWTs carried the claims, and Proof Key for Code Exchange (PKCE) made it secure. Today, with evolving AI, agents act on behalf of users and seek multiple accesses across different resources to execute a task. And that is when you’ll hit the gap. The user has an identity,...
Introducing Okta Journeys: A Better Way for Developers to Learn Identity

Learning identity management is hard enough. Navigating Okta’s documentation to build something shouldn’t be. If you’ve ever lost an afternoon stitching together how-to guides, product docs, and scattered blog posts just to figure out where to start, you’re not alone – and we’ve heard you, loudly and repeatedly. Today, we’re excited to announce the official launch of Journeys: a new way to navigate Okta documentation built around the tasks you’re actually trying to accomplish. What...
Build, Test, and Publish a Cross App Access App in the Okta Integration Network
Cross App Access (XAA) lets your application request data from another vendor’s API on behalf of a signed-in enterprise user, without static API keys and without a separate consent prompt for every connection. If enterprises buy your software, supporting XAA turns your integration into something their IT team can govern centrally. This guide walks through building XAA support into your app or Model Context Protocol (MCP) server, testing the token exchange with Okta’s developer tools,...